GNTECH Infrastructure Part 09: Docker Compose and Traefik for Private Applications
Route one application through a socket-free Traefik gateway, verify TLS with a local trust anchor, and check that a container replacement keeps application data.
Route one application through a socket-free Traefik gateway, verify TLS with a local trust anchor, and check that a container replacement keeps application data.
Build one controlled browser access path, test who is denied as carefully as who is allowed, and keep recovery independent of Cloudflare and your identity provider.
Protect the routing boundary before opening services: inventory firewall ownership, apply a deliberately scoped IPv4 forwarding and NAT lab, test negative paths, and keep a verified rollback.
Build the host before the routers: choose a storage layout, preserve provider WAN connectivity, prepare isolated bridges, and prove emergency recovery.
Route only required workload subnets and keep host recovery outside the tunnel.
Build an isolated AD DS lab with integrated DNS, a second domain controller, validation checks, and a clear production boundary.
A staged design for synchronizing a small, deliberate set of identities and validating SSO, MFA, monitoring, and recovery before expanding scope.
Before deploying routers and VMs, define trust boundaries, IP ownership, management recovery, and a testable rollout plan.
A staged, console-first tutorial for a Hetzner Proxmox host with two routed CHR transit networks and a separate NATed private VM LAN.
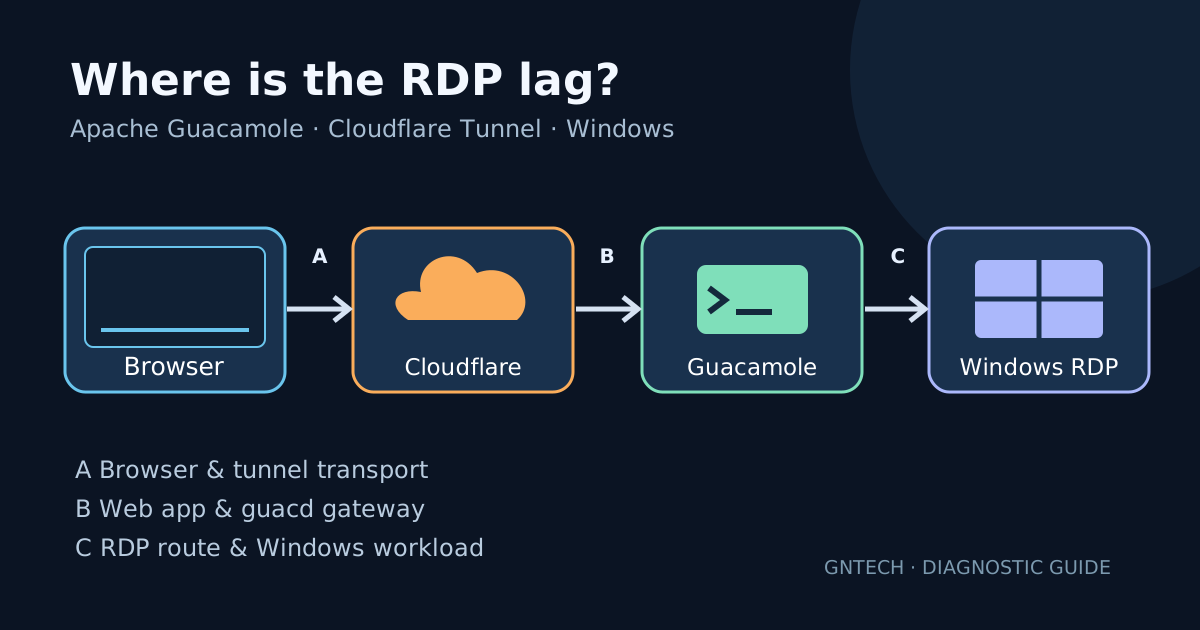
Trace browser-to-tunnel, Guacamole-to-guacd, and guacd-to-Windows paths before changing settings. Includes safe diagnostics and an A/B test worksheet.